AI-Assisted Discovery
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
Web Application Penetration Testing
Modern web applications handle sensitive data, business-critical workflows, APIs, authentication, payments, and integrations. A single vulnerability can expose customer information, compromise accounts, or interrupt business operations.
Our **Web Application Penetration Testing** service simulates realistic attack scenarios to identify security weaknesses before they can be exploited.
We combine **automated security testing, manual penetration testing, business-logic analysis, and expert validation** to provide findings that your development and security teams can actually act on.
Powered by our AI + Human Penetration Testing Platform: machine-speed analysis guided by expert testers who prove real-world risk.
How we work
We combine AI-powered analysis with senior penetration testers — delivering faster coverage and the human judgment attackers still require.
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
Expert testers confirm real impact, chain findings, and uncover business-logic flaws tools alone miss.
Risk is ranked by exploitability and business harm — so your team fixes what matters first.
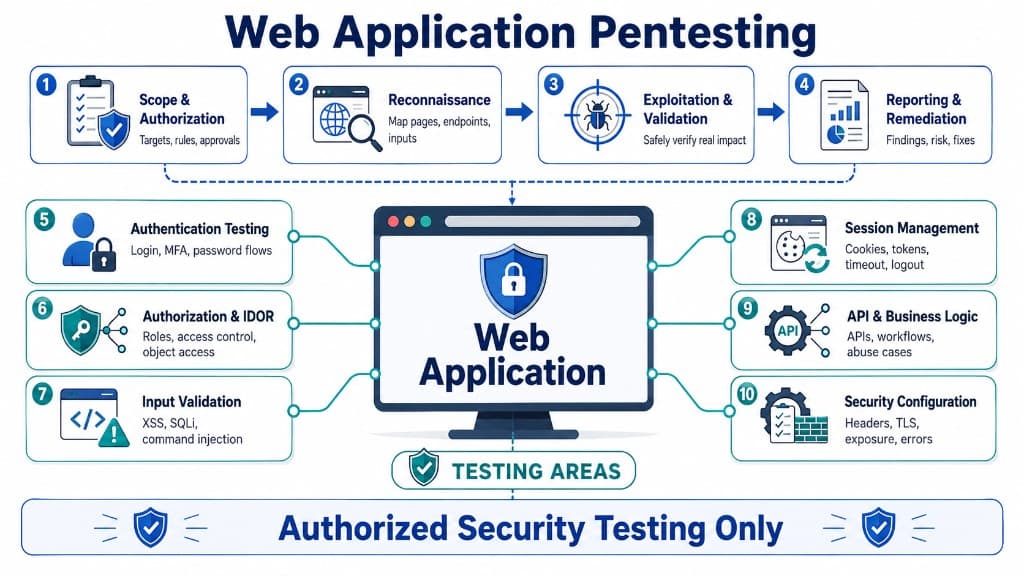
Prevent unauthorized users from gaining access to accounts.
Ensure users can only access the resources and actions they are authorized to use.
Prevent user input from becoming executable commands, scripts, or database queries.
Protect the services and data powering your web application. API testing is aligned with common OWASP API Security risks.
Prevent stolen or manipulated sessions from being used to hijack user accounts.
Protect not only your application code, but also your business processes.
1. Scope
Agree targets, roles, and rules of engagement.
2. Discover
Map pages, APIs, and the attack surface.
3. Map
Chart users, workflows, and critical functions.
4. Test
Manual testing across auth, APIs, and logic.
5. Validate
Prove impact safely with evidence.
6. Analyze
Score risk by exploitability and business harm.
7. Report
Deliver findings your team can act on.
8. Fix & Retest
Verify remediation after you patch.
AI / Scanners Alone
GET /api/users/123 HTTP/1.1
Host: app.example.com

HTTP/1.1 200 OK
AI + Human Testing
GET /api/users/124 HTTP/1.1
Authorization: Bearer <session>

User ID changed. Another user's data returned.
Attackers don't follow the rules. We test workflows, permissions, and business logic scanners never see. Built on our AI + Human Penetration Testing Platform.
Learn How We ThinkA clear view of risk for leadership, without the noise.
Every issue is confirmed, reproducible, and in scope.
Know what to fix first based on real business impact.
Requests, responses, and steps your developers can follow.
Practical fix recommendations, not generic scanner text.
We verify patches and check that fixes did not create new issues.
Whether you are preparing for a production release, reviewing an existing application, or strengthening your security program, penetration testing provides a realistic view of your application's security posture.