AI-Assisted Discovery
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
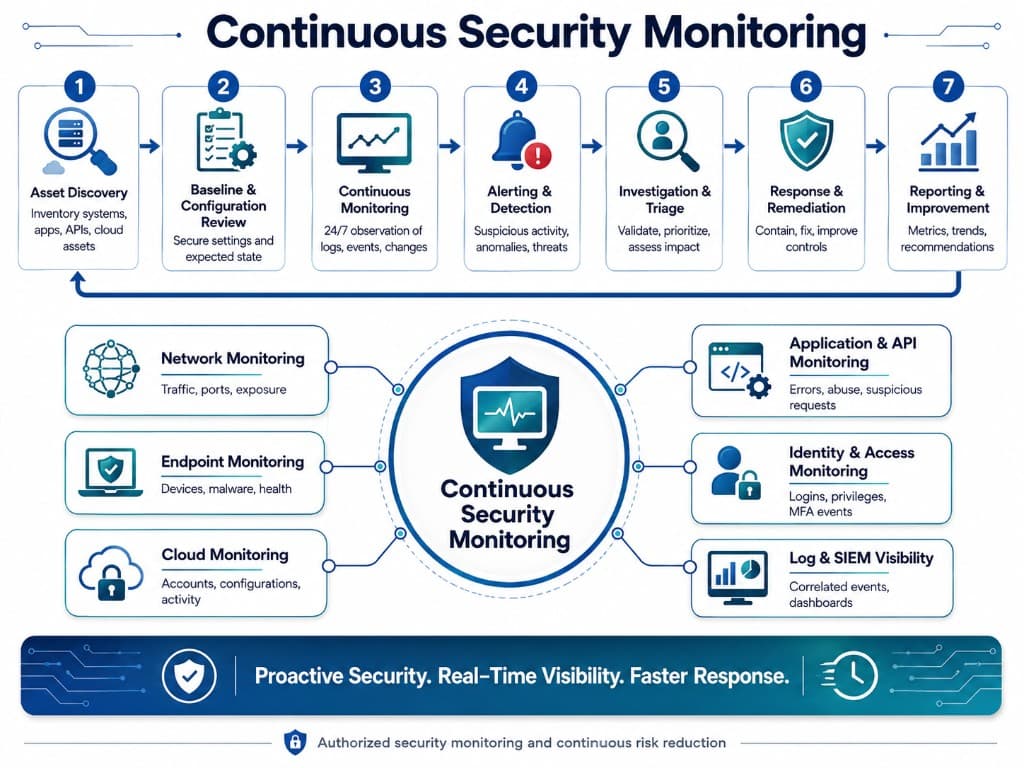
Continuous Security Monitoring
Move beyond point-in-time tests. Continuous Security Monitoring keeps watch over your assets, alerts on real risk, and helps your team respond before issues become incidents.
Powered by our AI + Human Penetration Testing Platform: machine-speed analysis guided by expert testers who prove real-world risk.
How we work
We combine AI-powered analysis with senior penetration testers — delivering faster coverage and the human judgment attackers still require.
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
Expert testers confirm real impact, chain findings, and uncover business-logic flaws tools alone miss.
Risk is ranked by exploitability and business harm — so your team fixes what matters first.
1. Asset Discovery
Inventory systems, apps, APIs, and cloud assets.
2. Baseline Review
Secure settings and expected state.
3. Continuous Monitoring
24/7 observation of logs, events, and changes.
4. Alerting & Detection
Suspicious activity, anomalies, and threats.
5. Investigation & Triage
Validate, prioritize, and assess impact.
6. Response & Remediation
Contain, fix, and improve controls.
7. Reporting & Improvement
Metrics, trends, and recommendations.
AI / Scanners Alone
Last pentest: 11 months ago
New subdomain published: api-staging.example.com
Open port: 8443

Status: Unknown risk until next annual test
AI + Human Testing
Asset change detected: api-staging.example.com
Exposure alert: public service on 8443
Triage: high priority
Response: contain + harden within hours
Annual assessments leave gaps between engagements. Continuous monitoring closes that window with real-time visibility and faster response. Built on our AI + Human Penetration Testing Platform.
Learn How We ThinkLive asset inventory, open findings, and severity breakdown.
Critical issue alerts via Slack, email, or ticketing.
Validate, prioritize, and assess impact with clear context.
Contain, fix, and improve controls with actionable steps.
New findings, resolved issues, and posture trends.
Metrics and recommendations that tighten security over time.
Stop relying on annual tests alone. Get continuous visibility into your security posture.