AI-Assisted Discovery
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
API Security Testing
We test REST and GraphQL APIs for authentication flaws, broken object authorization, token weaknesses, and abuse paths scanners miss — then help your team fix what matters.
Powered by our AI + Human Penetration Testing Platform: machine-speed analysis guided by expert testers who prove real-world risk.
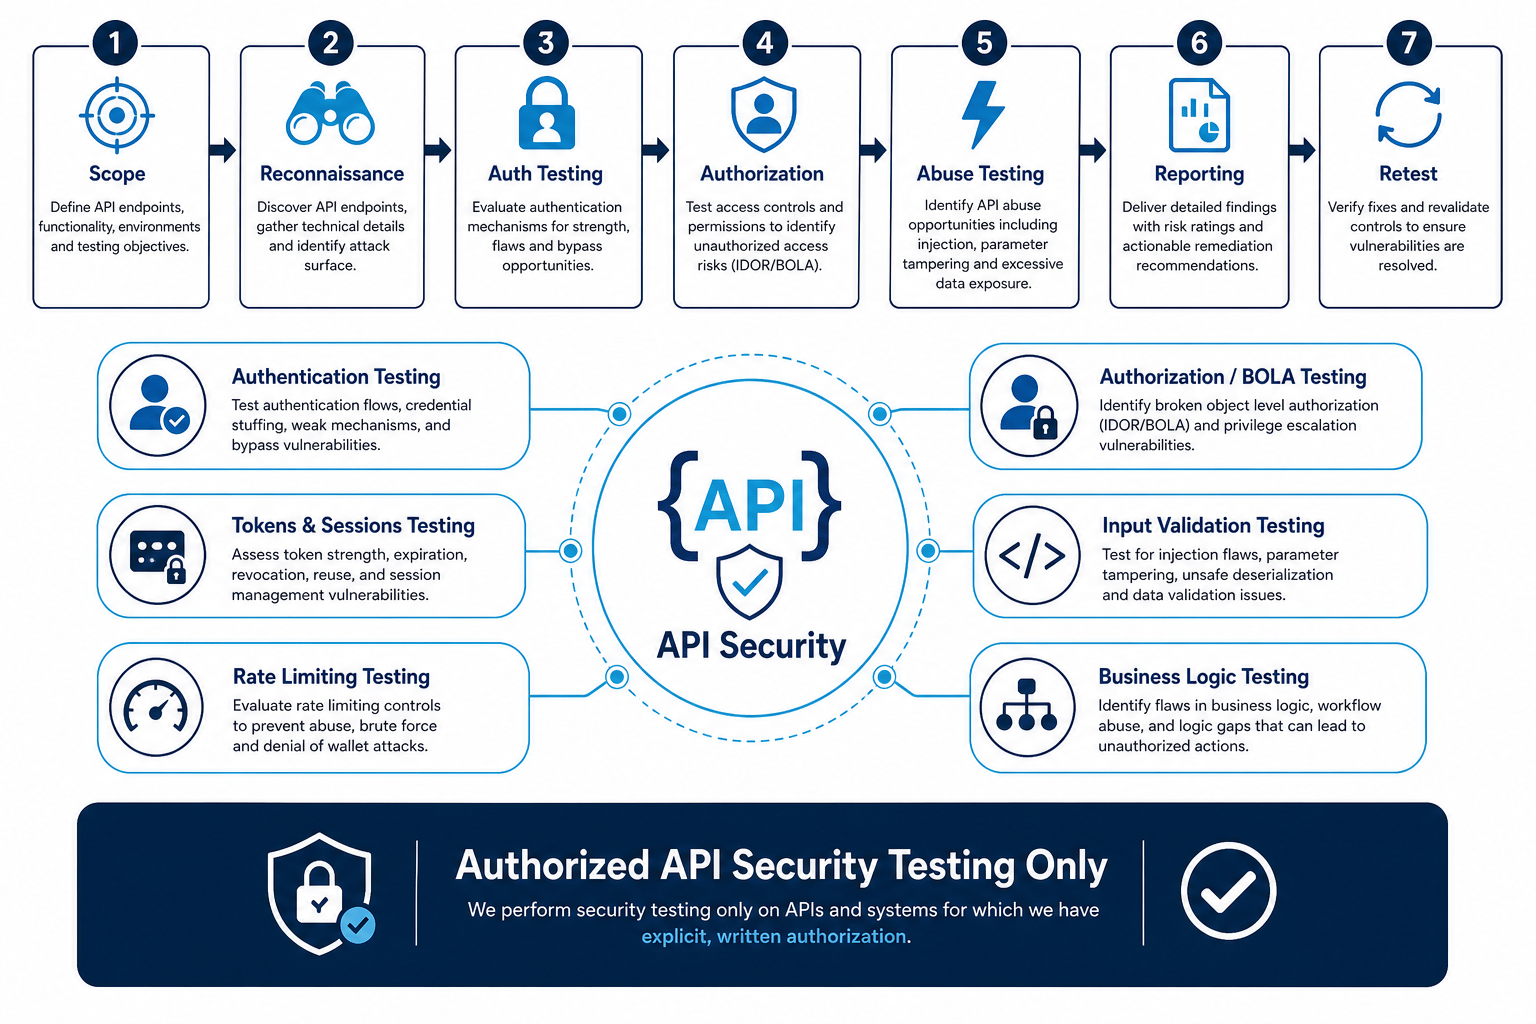
How we work
We combine AI-powered analysis with senior penetration testers — delivering faster coverage and the human judgment attackers still require.
Intelligent automation accelerates reconnaissance, pattern matching, and coverage across large attack surfaces.
Expert testers confirm real impact, chain findings, and uncover business-logic flaws tools alone miss.
Risk is ranked by exploitability and business harm — so your team fixes what matters first.
Login, MFA, identity.
Object and role access control.
Token security and lifecycle.
Safe handling of untrusted input.
Abuse resistance.
Protect business processes behind APIs.
1. Scope
APIs, environments, roles, and rules.
2. Discover
Map endpoints, schemas, and auth flows.
3. AuthN
Test identity and credential handling.
4. AuthZ
Probe BOLA/IDOR and privilege boundaries.
5. Abuse
Rate limits, mass assignment, logic flaws.
6. Report
Prioritized findings with evidence.
7. Retest
Confirm vulnerabilities are resolved.
AI / Scanners Alone
GET /api/orders/4821
Authorization: Bearer <user-token>

HTTP/1.1 200 OK
AI + Human Testing
GET /api/orders/4822
Authorization: Bearer <same-user-token>

Another customer's order returned.
Scanners often stop at HTTP 200. We ask whether this user should be allowed to perform that action — and prove the impact. Built on our AI + Human Penetration Testing Platform.
Talk to a Security ExpertAPI risk for leadership without the noise.
Confirmed issues with reproducible requests.
Object and role access failures clearly demonstrated.
Know which endpoints to fix first.
Server-side checks and token hardening notes.
We verify patches after remediation.
Authorized API security testing — authentication, authorization, tokens, abuse, and business logic — with remediation and retest.